Clinic phone lines
Answer, verify, and route without exposing PHI to a non-compliant vendor.


Production voice agents for clinics and pharmacies on compliant telephony (signed BAA, call-recording consent, and PHI redaction) so the automation answering your phones can be trusted with PHI.
Trusted by global innovators









A healthcare voice AI agent needs a compliant telephony layer, because most voice bots record without consent, store raw audio full of names and dates of birth, and run on vendors that won't sign a BAA. Agnotic Technologies builds that foundation for every voice workflow.
Every call runs under a BAA, opens with a recording-consent disclosure and passes through PHI redaction before transcripts are stored, so the layer stays audit-ready.
A compliant telephony spine: consented recording, real-time ASR, a redaction pass that strips identifiers before storage, policy-guarded actions, and audit logs.
The controls that make an agent safe on a healthcare line.
Carrier, ASR/TTS, and storage all run under a BAA: PHI never touches a non-compliant component.
Calls open with a jurisdiction-aware consent disclosure, honor two-party-consent states, and log the response before recording.
Names, DOBs, MRNs, and card numbers are masked in transcripts and stored audio, so logs never hold raw identifiers.
Verifies the caller before disclosing PHI, then performs only role-permitted actions and posts results to the EHR, pharmacy system, or CRM over FHIR R4 or vendor APIs.
Who runs it
Answer, verify, and route without exposing PHI to a non-compliant vendor.
Refill status and pickup questions with consented recording and redaction.
Confirmations that log consent and honor opt-out.
Answer coverage questions after verifying the caller.
One compliant voice layer across sites, each with its own consent policy.
Absorb overflow calls with the same compliance posture.
Go-live checklist
A healthcare voice agent is ready to go live when every item is checked and signed off by its owner. Use this healthcare voice agent checklist in the final review before the first patient call; any open item keeps the agent in testing.
Framed as controls, not invented metrics, each a property of the stack you can verify.
Health Insurance Portability and Accountability Act
Protect PHI with privacy-first architecture, encrypted storage and transmission, strict access controls, and traceable audit logs.
General Data Protection Regulation
Implement lawful consent flows, data minimization, retention controls, and secure processing for sensitive health data.
Fast Healthcare Interoperability Resources
Enable standardized health data exchange across apps, care teams, and systems through standards-based FHIR APIs.
Health Level Seven International
Support enterprise-grade interoperability with HL7-based integrations for records, events, and clinical messaging workflows.
Health Information Trust Alliance
Align security programs to healthcare-specific control and risk management practices trusted by providers and ecosystem partners.
Health Information Technology for Economic and Clinical Health Act
Design with breach notification readiness, digital record safeguards, and operational controls that support regulated care programs.
FDA Software as a Medical Device
Plan software quality, traceability, and documentation pathways for products that may require SaMD review and submission.
Medical Device Regulation (European Union)
Prepare EU market-ready processes for risk classification, evidence tracking, and lifecycle governance under MDR expectations.
Substance Abuse and Mental Health Services Administration
Apply confidentiality controls and consent-aware sharing models for behavioral and mental health data experiences.
Standards
Four stages: consented capture, redaction and understanding, a permitted action, and a logged write-back.
The agent answers, plays the recording-consent disclosure, logs the response, then streams ASR after consent and identity.
A redaction pass masks identifiers in real time, then intent recognition determines the need under role-scoped guardrails.
The agent performs only policy-allowed actions (status lookups, confirmations, routing) escalating anything clinical or out-of-scope.
Outcomes post to the EHR or pharmacy system over FHIR R4 or vendor APIs, and the consented, redacted call is audit-logged.
Short facts we design around, each linked to its primary source.
A HIPAA covered entity may share protected health information with a business associate, such as a software vendor, only under a business associate agreement that commits the vendor to safeguard it.
Source: 45 CFR 164.502(e) and 164.504(e) (eCFR)Before disclosing protected health information under the HIPAA Privacy Rule, apart from disclosures under 164.510, a covered entity must verify the identity and authority of a requester whose identity or authority it does not already know.
Source: 45 CFR 164.514(h) (eCFR)FCC rules bar calls to a wireless number using an artificial or prerecorded voice unless the call is made for emergency purposes or with the prior express consent of the called party.
Source: 47 CFR 64.1200(a)(1) (eCFR)In Declaratory Ruling FCC 24-17, released February 8, 2024, the FCC confirmed that the TCPA's restrictions on the use of an artificial or prerecorded voice cover current AI technologies that generate human voices.
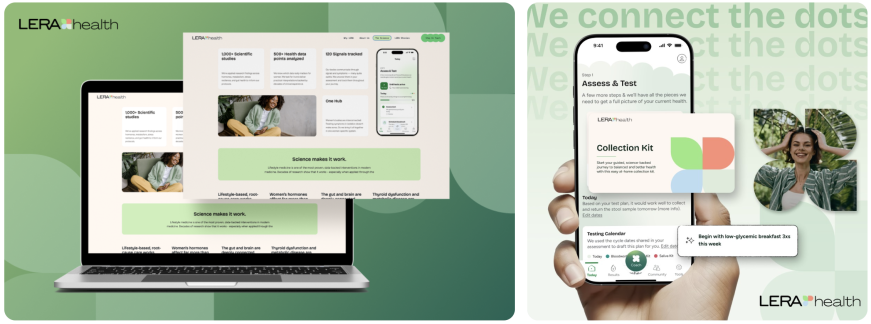
Source: FCC Declaratory Ruling FCC 24-17, CG Docket No. 23-362Related proof of compliant, AI-assisted delivery, not this specific voice stack. On Lera Health we built the privacy-first data layer and consented data flows that mirror this BAA-backed, audit-logged foundation.
Compliance is the product here: four controls built into the telephony layer itself.
BAA-backed carriers and models, end-to-end encryption, real-time redaction, and configurable retention.
Role-scoped escalation: clinical, complex, or low-confidence calls transfer to staff with the redacted transcript.
Each action ties back to the consent record, verified identity, and authorizing intent.
Consent, verification, redaction, and write-backs are time-stamped in tamper-evident logs.
Bring us the workflows to automate; we'll return a telephony and compliance scope (BAA, consent, redaction, audit) before a live call.
contact@agnotic.com
Partnerships
contact@agnotic.com