


SOC 2 readiness engineering
Enterprise health buyers ask for a SOC 2 report before they sign, and most of the controls it covers live in your code, cloud and release process. Agnotic Technologies builds the access control, change management, logging and evidence automation your auditor will test.
Trusted by global innovators









What is SOC 2 for healthcare software?
SOC 2 for healthcare software is the set of engineering controls a health tech product needs before an independent CPA firm examines it against the AICPA Trust Services Criteria. When the product also handles PHI, the same access, logging and encryption controls serve the HIPAA Security Rule, so one control set supports both reviews.
Controls engineering owns
Which SOC 2 controls does engineering own?
Your auditor sets the scope, but most technical controls are built and run by the product team. This is the share we build, with the evidence each one leaves and where it overlaps with HIPAA.
| Control area | What we build | Evidence for the auditor | HIPAA Security Rule overlap |
|---|---|---|---|
| Logical access | SSO, multi-factor sign-in, role-based access and automated joiner and leaver steps | User lists, access review records and offboarding tickets | Access control and person or entity authentication |
| Change management | Reviewed pull requests, protected branches, automated tests and approved deployments | Pull request history, CI results and release records | Integrity of ePHI |
| Logging and monitoring | Central logs, an audit trail of data access and alerts routed to an owner | Alert rules, log retention settings and incident tickets | Audit controls |
| Encryption | Encryption at rest and in transit with managed keys | Encryption and key management configuration | Encryption and transmission security |
| Backup and recovery | Automated backups and scheduled restore tests | Backup reports and restore test records | Contingency plan |
| Vendor management | A subprocessor list kept in step with the code and infrastructure | Vendor list with agreements, including BAAs where PHI flows | Business associate contracts |
This table shows the engineering share of a SOC 2 program, not a full control set. Agnotic builds and documents the controls; an independent CPA firm performs the examination.
How does Agnotic build SOC 2 readiness?
A controls-first approach to SOC 2 readiness engineering, mapping the Trust Services Criteria to working controls and the evidence that proves them.
Readiness Assessment
We scope your Trust Services Criteria, map current controls and gaps, and define the control set your report will attest to.
Control Design
We design access, change-management, and monitoring controls around your architecture and risk profile, not a generic checklist.
Implementation & Evidence
We implement controls and connect your cloud, code and identity systems to a compliance automation platform such as Vanta, Drata or Sprinto, so evidence collects as you work instead of being rebuilt before the audit.
Audit Support & Monitoring
We support the Type I and Type II audit windows, remediate findings, and keep controls monitored between reports.
App gallery
View AllLera Health
Controls-first delivery
A repeatable process that builds SOC 2 controls for startups and growing health tech teams into every stage, and keeps them verifiable across the Type II observation period.
Scoping & Gap Analysis
We define the Trust Services Criteria in scope, map your systems and data flows, and identify control gaps before build.
Control Implementation
Least-privilege access, change management, encryption, and logging are stood up as foundational controls with owners assigned.
Evidence Automation
We instrument automated evidence collection (access reviews, change logs, monitoring alerts) so the audit trail builds itself.
Audit & Continuous Monitoring
We support the auditor through Type I and Type II, remediate exceptions, and monitor controls between reporting periods.
How do SOC 2 and HIPAA
share one architecture?
One layered control set serves both: least-privilege access, encryption in transit and at rest, change management and monitoring, mapped to the SOC 2 Trust Services Criteria and to the HIPAA Security Rule safeguards.
Which rules shape SOC 2 work in healthcare?
Short facts from the AICPA and the HIPAA Security Rule, each linked to its primary source.
A SOC 2 report is an assurance report, issued by a CPA, on a service organization's controls relevant to security, availability, processing integrity, confidentiality or privacy.
Source: AICPA & CIMAThe AICPA's 2017 Trust Services Criteria, with points of focus revised in 2022, are the control criteria used to evaluate and report on controls over the security, availability, processing integrity, confidentiality or privacy of information and systems.
Source: AICPA & CIMA, 2017 Trust Services Criteria (revised points of focus, 2022)The HIPAA Security Rule requires administrative, physical and technical safeguards for electronic protected health information.
Source: 45 CFR Part 164 Subpart C (eCFR)
Which other standards sit next to SOC 2?
HIPAA
Health Insurance Portability and Accountability Act
Protect PHI with privacy-first architecture, encrypted storage and transmission, strict access controls, and traceable audit logs.
GDPR
General Data Protection Regulation
Implement lawful consent flows, data minimization, retention controls, and secure processing for sensitive health data.
FHIR
Fast Healthcare Interoperability Resources
Enable standardized health data exchange across apps, care teams, and systems through standards-based FHIR APIs.
HL7
Health Level Seven International
Support enterprise-grade interoperability with HL7-based integrations for records, events, and clinical messaging workflows.
HITRUST
Health Information Trust Alliance
Align security programs to healthcare-specific control and risk management practices trusted by providers and ecosystem partners.
HITECH
Health Information Technology for Economic and Clinical Health Act
Design with breach notification readiness, digital record safeguards, and operational controls that support regulated care programs.
SaMD
FDA Software as a Medical Device
Plan software quality, traceability, and documentation pathways for products that may require SaMD review and submission.
MDR (EU)
Medical Device Regulation (European Union)
Prepare EU market-ready processes for risk classification, evidence tracking, and lifecycle governance under MDR expectations.
SAMHSA
Substance Abuse and Mental Health Services Administration
Apply confidentiality controls and consent-aware sharing models for behavioral and mental health data experiences.
Featured case study
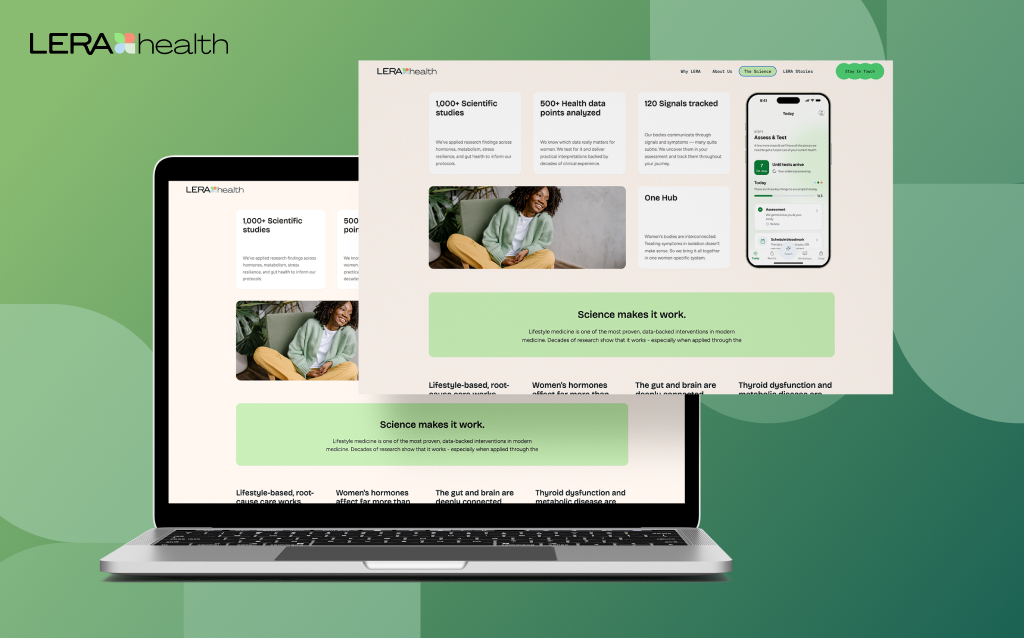
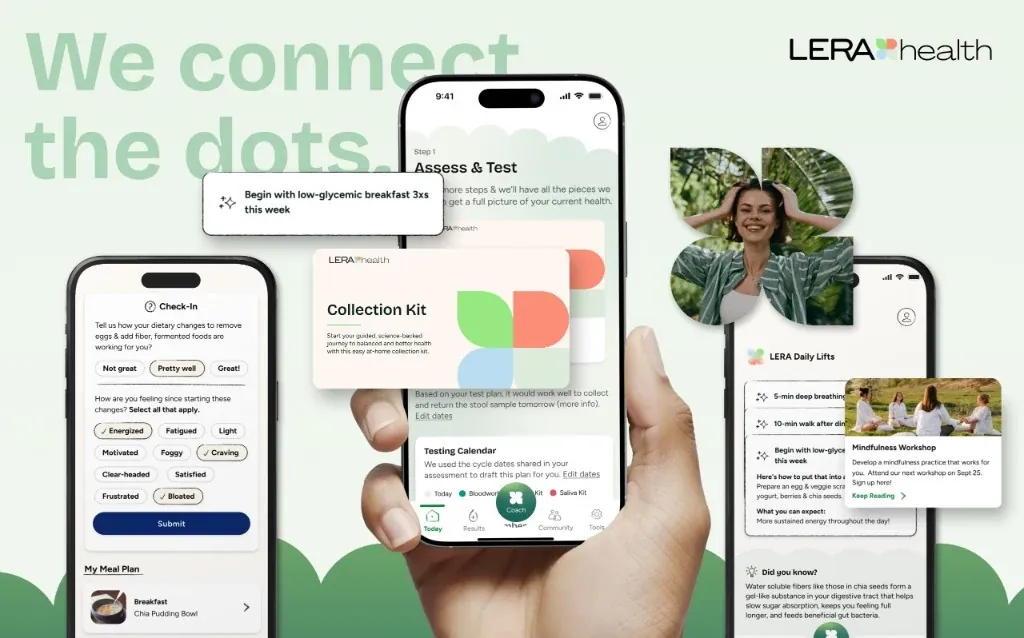
Read Case StudyLera Health: compliant health platform
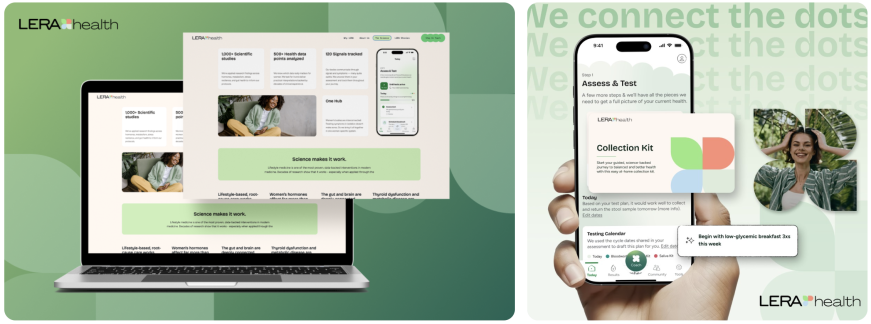
Related proof of controls-first delivery: for Lera Health we built a privacy-first data layer with least-privilege access, encryption, and audit-ready logging, the same control foundation a SOC 2 program attests to.
SOC 2 readiness FAQs
Build compliantly