


HIPAA compliance consulting
Advisory engagements for teams that need HIPAA clarity: gap assessments, Security Rule risk analysis, BAA and policy support, and a pragmatic remediation roadmap you can act on, whether or not we build the product.
Trusted by global innovators









Our consulting approach
We meet you where you are. Rather than assuming a rebuild, our consulting engagements assess your current posture against the HIPAA Privacy, Security, and Breach Notification Rules, quantify the real risks, and hand you a prioritized, pragmatic roadmap, so you invest in the controls that actually reduce exposure.
Product risk analysis
What does a HIPAA risk analysis cover in a software product?
A HIPAA risk analysis covers every place your product stores, copies or sends ePHI, not only the main database. Agnotic Technologies maps backups, logs, analytics copies, queues, third-party and AI APIs, support tools and test data, with the threat, control and evidence for each.
| Where ePHI ends up | Example threat | Typical control | Evidence to keep |
|---|---|---|---|
| Primary database | Over-broad access by staff or a compromised service account | Role-based access, encryption at rest, least-privilege service accounts | Access review records and the encryption configuration |
| Backups and snapshots | A snapshot shared or restored outside the production account | Encrypted backups, restricted restore rights, retention limits | Backup policy, restore test results and access logs |
| Application logs and error trackers | Request bodies or patient names written into logs | Log redaction, field allowlists and short retention | Logging standard and a sample review of log content |
| Analytics and BI copies | A full copy of production data in a reporting tool with wide access | De-identified or minimum necessary extracts, separate access groups | Data flow diagram and the extract field list |
| File and document storage | Public links or misconfigured buckets exposing uploads | Private storage, signed short-lived links, malware scanning | Storage policy settings and access logs |
| Message queues and event streams | Payloads kept unencrypted long after they are processed | Encryption in transit and at rest, retention set per topic | Queue configuration and retention settings |
| AI and other third-party APIs | ePHI sent to a vendor with no business associate agreement | BAA in place before any ePHI is sent, or data removed from prompts | Vendor list with BAA status and data sent to each |
| Support and email tools | Screenshots or record details pasted into tickets and email | Support workflow that references record IDs, tool access limits | Support procedure and the BAA or exclusion for each tool |
| Test and staging data | Production records copied into environments with weaker controls | Synthetic or de-identified test data as the default | Test data policy and the approval for any exception |
Run the analysis again when the product adds a vendor that touches ePHI, a feature that stores new ePHI, a new data flow or a new hosting region. The NIST SP 800-66r2 step method is set out on our HIPAA Security Rule checklist.
Framework
A structured advisory approach: assess where you stand, quantify risk, and deliver a roadmap and the documentation you need to act on it.
Gap Assessment
We assess your systems, policies, and data flows against the HIPAA Privacy and Security Rules to find where you stand.
Risk Analysis
We run a Security Rule risk analysis, quantify likelihood and impact, and prioritize remediation by real exposure.
Roadmap & Policies
We deliver a prioritized remediation roadmap plus the policies, procedures, and BAA templates you need in place.
Advisory & Audit Support
We support remediation, staff readiness, and audit or partner due diligence with ongoing advisory.
App gallery
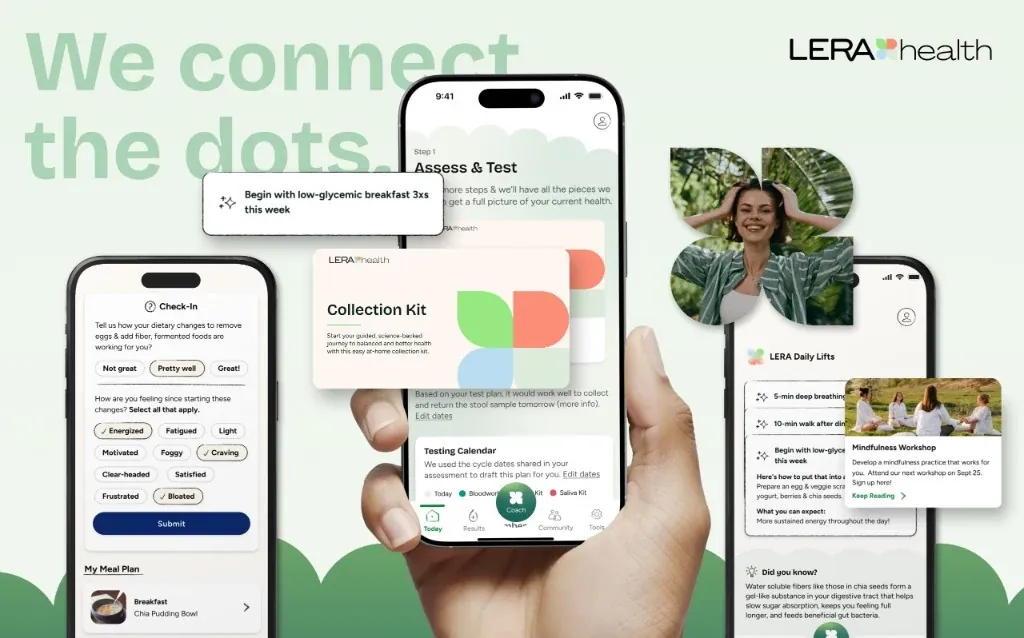
View AllLera Health
Advisory engagement
A clear, documented engagement that turns HIPAA uncertainty into a prioritized action plan, with the risk analysis and policies auditors and partners expect.
Scoping & Discovery
We define your covered-entity or business-associate role, scope, and the systems and data flows in play.
Risk Analysis & Gap Assessment
We assess controls against the Security Rule and run a documented risk analysis with prioritized findings.
Roadmap & Documentation
We deliver a remediation roadmap, policy and procedure set, and BAA guidance you can act on.
Remediation & Readiness Support
We advise through remediation and prepare you for audits, partner due diligence, or certification.
Risk & remediation
roadmap
A clear picture of your HIPAA posture: a documented Security Rule risk analysis, prioritized gaps, and a pragmatic remediation roadmap across policy, process, and technical controls.
Featured case study
Read Case StudyLera Health: compliant health platform
Related proof of compliance depth: for Lera Health we brought privacy-by-design architecture, risk-aware data flows, and audit-ready controls together, the same rigor our advisory engagements help teams reach.

Frequently Asked Questions
Get a HIPAA assessment
Tell us your role and systems, and we'll scope a gap assessment, risk analysis, and remediation roadmap you can act on.
Build compliantly